Exploit Hound
A hosted exposure-management platform that discovers assets, correlates vulnerabilities, ranks remediation by the attack paths it removes, and verifies fixes by re-checking — across every customer environment.
The problem
Vulnerability scanners are good at producing findings and bad at deciding. Ranking by CVSS alone sends technicians after issues that don’t matter while real paths to critical systems stay open — and a remote-management tool reporting “patched” isn’t proof that anything changed.
Why existing tools fell short
Vulnerability scanners rank findings by severity score, which produces long lists without telling a technician which fix removes the most real risk — and they generally accept a patch tool’s “success” as proof.
The solution
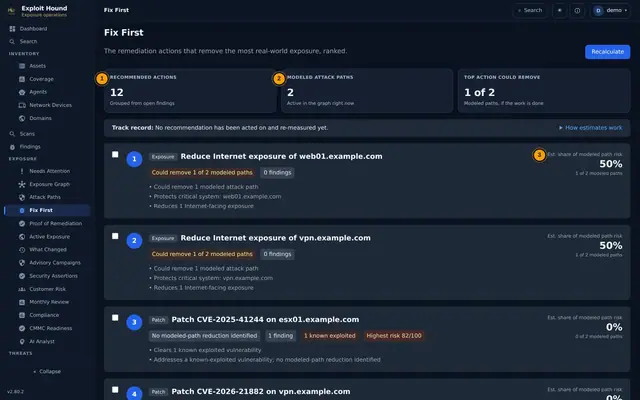
Exploit Hound builds a customer-scoped exposure graph from discovered assets and findings, then groups work into technician-sized actions ranked by how many modeled attack paths each one removes. After a fix, it re-checks to verify the exposure is actually gone.
Threat Radar adds outside context: vulnerabilities confirmed as exploited in the wild (CISA KEV) and those with the highest predicted likelihood of exploitation (FIRST EPSS).
- “Fix First” — findings grouped into technician actions, ranked by attack paths removed
- Asset discovery: external surface, onsite LAN probe, and endpoint agents
- Remediation verified by re-checking, not by trusting a tool’s “success”
- Threat Radar: known-exploited and most-likely-exploited vulnerabilities
- Multi-tenant MSP console with per-customer exposure graphs
Engineering involved
Drawn from the product’s own public documentation and trust pages. Only components the product publicly documents are listed.
- Architecture
- Hosted management with local collection: collectors and agents connect outbound over TLS, so no inbound connection to the customer network is required.
- Tenant isolation
- Every query is scoped to the tenant in the data model rather than only in the interface.
- Data & threat intelligence
- Correlates the CVE Program, NVD, FIRST EPSS, OSV, Exploit-DB, GitHub advisories, and CISA KEV.
- Collection
- External surface discovery, an onsite LAN probe, NetFlow, deception/honeypots, and an OS client for Linux, Windows, and macOS (macOS in beta) written in Go.
- Authentication
- Time-based one-time codes for accounts with two-factor enabled.
- AI integration
- An optional AI security analyst (Anthropic) that cannot trigger scanning or any state change.
- Integrations
- Identity, cloud, PSA, and RMM integrations (Entra ID, Google Workspace, AWS/Azure/Google Cloud, HaloPSA, ConnectWise, Autotask, NinjaOne, Datto, and more) are documented as in beta.
What makes it interesting
Prioritization is modeled, not scored. Ranking fixes by attack paths removed — instead of by severity number — turns a list of thousands into a short, defensible to-do list, and the “verified by re-checking” step closes the loop that most tooling leaves open.
Outcome
Not measured The core exposure workflow is generally available and the platform is in its founding beta program. No usage, revenue, or performance figures have been published, so none are claimed here.
Current status
Active Beta Working software in a public beta or early-access program — not yet generally available.
Exploit Hound’s core exposure workflow is generally available, and it runs a founding beta partner program. The product publishes which capabilities are generally available, which are in beta (notably identity, cloud, PSA, and RMM integrations), and which are not built. It states that there is no SOC 2 report, ISO 27001 certificate, or independent penetration test.
See it working
See the twelve-screen product tour from the running console (demonstration data) at exploithound.com/product-tour, or the public Threat Radar.
Want something similar?
Need a system like this, built around your own business? MyAppDone can design, build, deploy, and maintain an application tailored to your workflow.
Related projects
MailThreatZero
Problem: MSPs and multi-domain organizations pay per mailbox for filtering they can’t explain — when a message is blocked or delivered, nobody can show why.
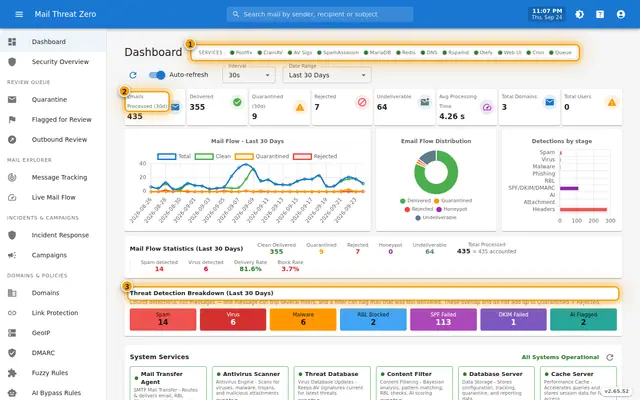
A managed email security gateway for MSPs and multi-domain organizations, with explainable multi-stage scoring, per-tenant policies, quarantine, and domain reputation monitoring — priced per protected domain rather than per mailbox.
- SMTP gateway with five scanning stages: reputation, authentication, malware, content, optional AI
- Explainable scoring: each stage’s weight and contribution to the verdict
- Monitor Mode, quarantine review and release, and message tracking
- Delegated MSP administration with tenant, domain, and read-only roles
- Domain reputation, DMARC aggregate reporting, and a REST API
OPNMGR
Problem: Managing dozens of firewalls means logging into each one to check health, back up configs, and apply updates — and hoping nothing drifted in between.
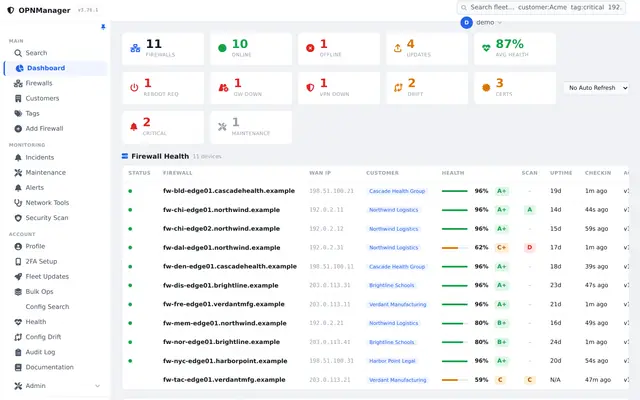
Self-hosted OPNsense fleet management for MSPs and IT teams: monitor every firewall, back up and diff configurations against an approved baseline, and roll out updates in safe, staged rings.
- Agent check-ins for gateways, VPN, CARP, services, and certificate expiry
- Configuration backups and drift detection against an approved baseline
- Update campaigns through canary, pilot, and production rings
- Incidents, maintenance windows, and grouping by customer and site
- Optional AI configuration review with secrets redacted
ClientSt0r
Problem: MSPs keep runbooks, assets, passwords, and tickets in separate rented products, so a technician opening a ticket has to hunt across systems for context.
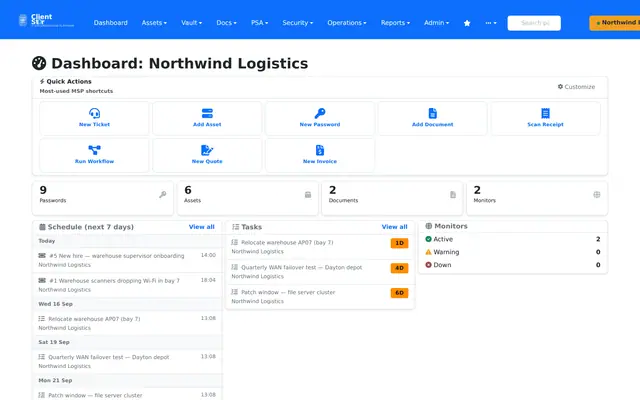
Self-hosted IT documentation and service desk for MSPs. A ticket opens with the client’s contract, the affected asset, the runbook, and the vault entries the technician needs — all in one database.
- Client documentation, assets, runbooks, and an encrypted password vault
- Opt-in service desk: queues, SLA timers, time entries, quotes, invoices, and contracts
- One organization per client, with parent/child organizations
- Enforced TOTP 2FA and optional Entra ID SSO or LDAP
- PSA and RMM integrations and a browser extension